All 31 Login Security answers
Answer
Does it work behind Cloudflare, or a load balancer?
Yes. Everything behind a proxy sees the proxy's address on every request, so a plugin that read the raw connection address would lock out the whole internet at once or nobody at all. This reads the headers Cloudflare and the common proxies set, in the right order, and falls back to the connection address. A server that writes IPv4 addresses the IPv6 way, as ::ffff:203.0.113.7, is read as 203.0.113.7, so Cloudflare or a proxy written that way is now recognised.
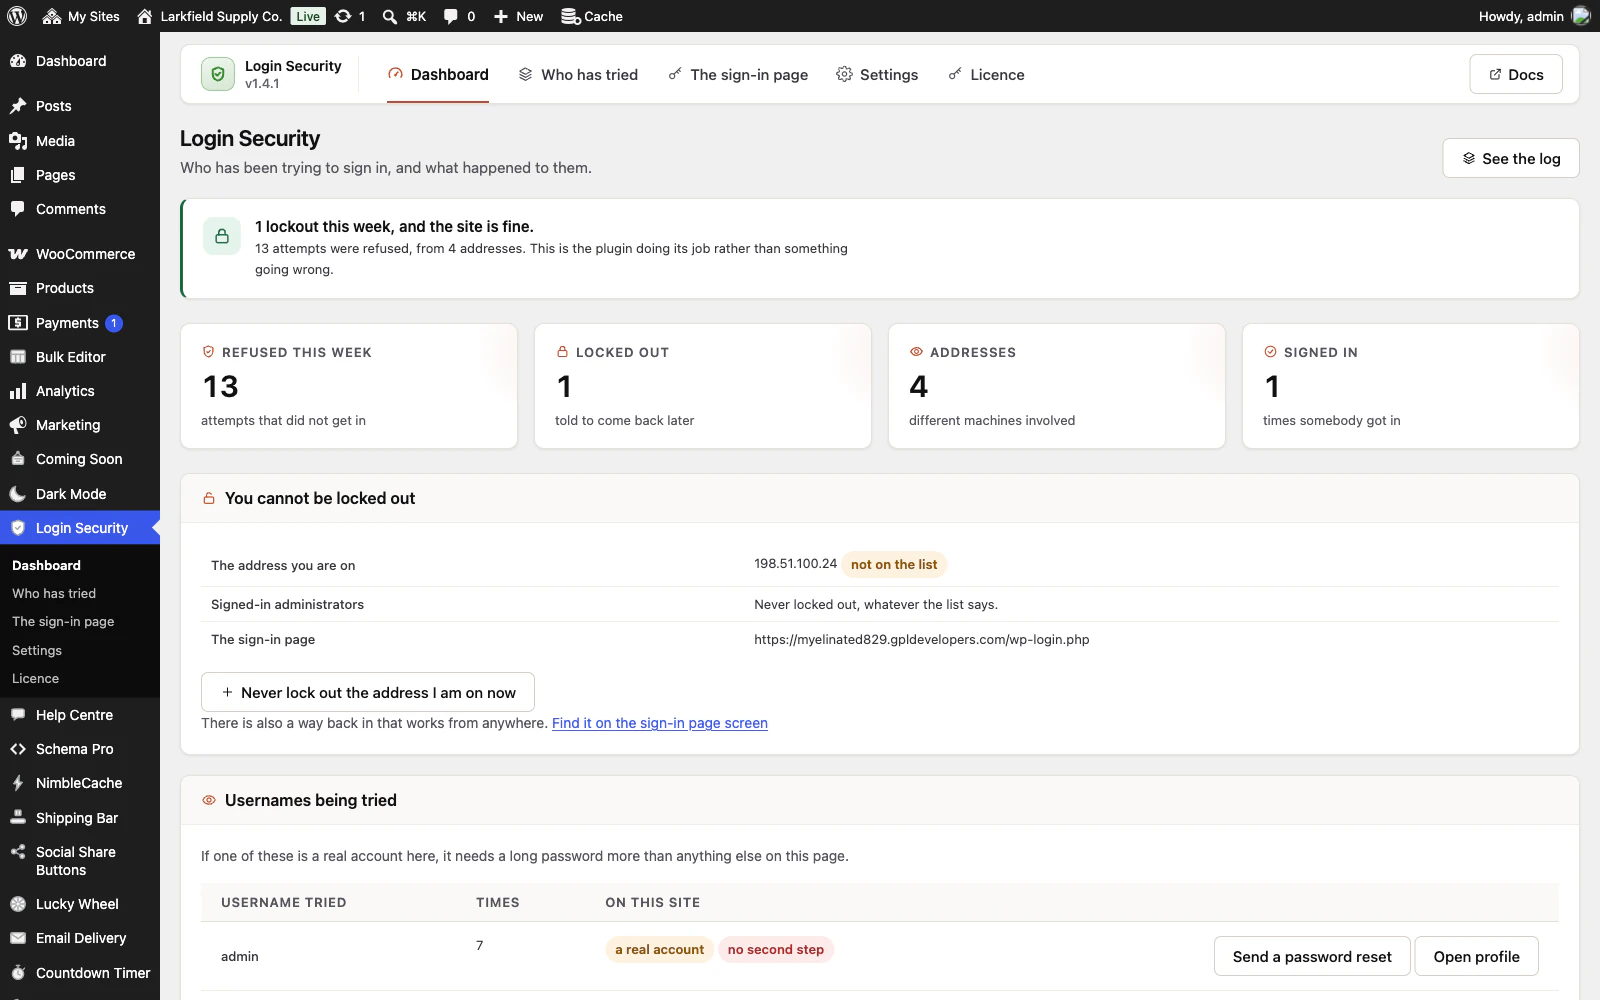
Before it was, every visitor on such a server looked like the proxy. The address trusted when you switched the plugin on was then the proxy's, such as 127.0.0.1 or a Cloudflare address, and it covered every visitor who came through that proxy: behind a proxy of your own, that was everybody, so nobody was locked out. Now each visitor has their own address and lockouts reach them, you included. If the Dashboard says the address you are on is not on the list, press Never lock out the address I am on now. The old line can come off Never locked out on the Settings screen: it no longer matches your visitors.
Check the first screen: it shows the address it thinks you are on. If that is your own address rather than a server's, it is reading them correctly.
Still stuck? Ask the developers who wrote it. We aim to reply within one business day.
 Login Security
Stop the machines guessing at your passwords, and see exactly who has been trying.
From $19 a year · every feature · 30-day refund