All 31 Login Security answers
Answer
I got an email about a lockout. Is my site hacked?
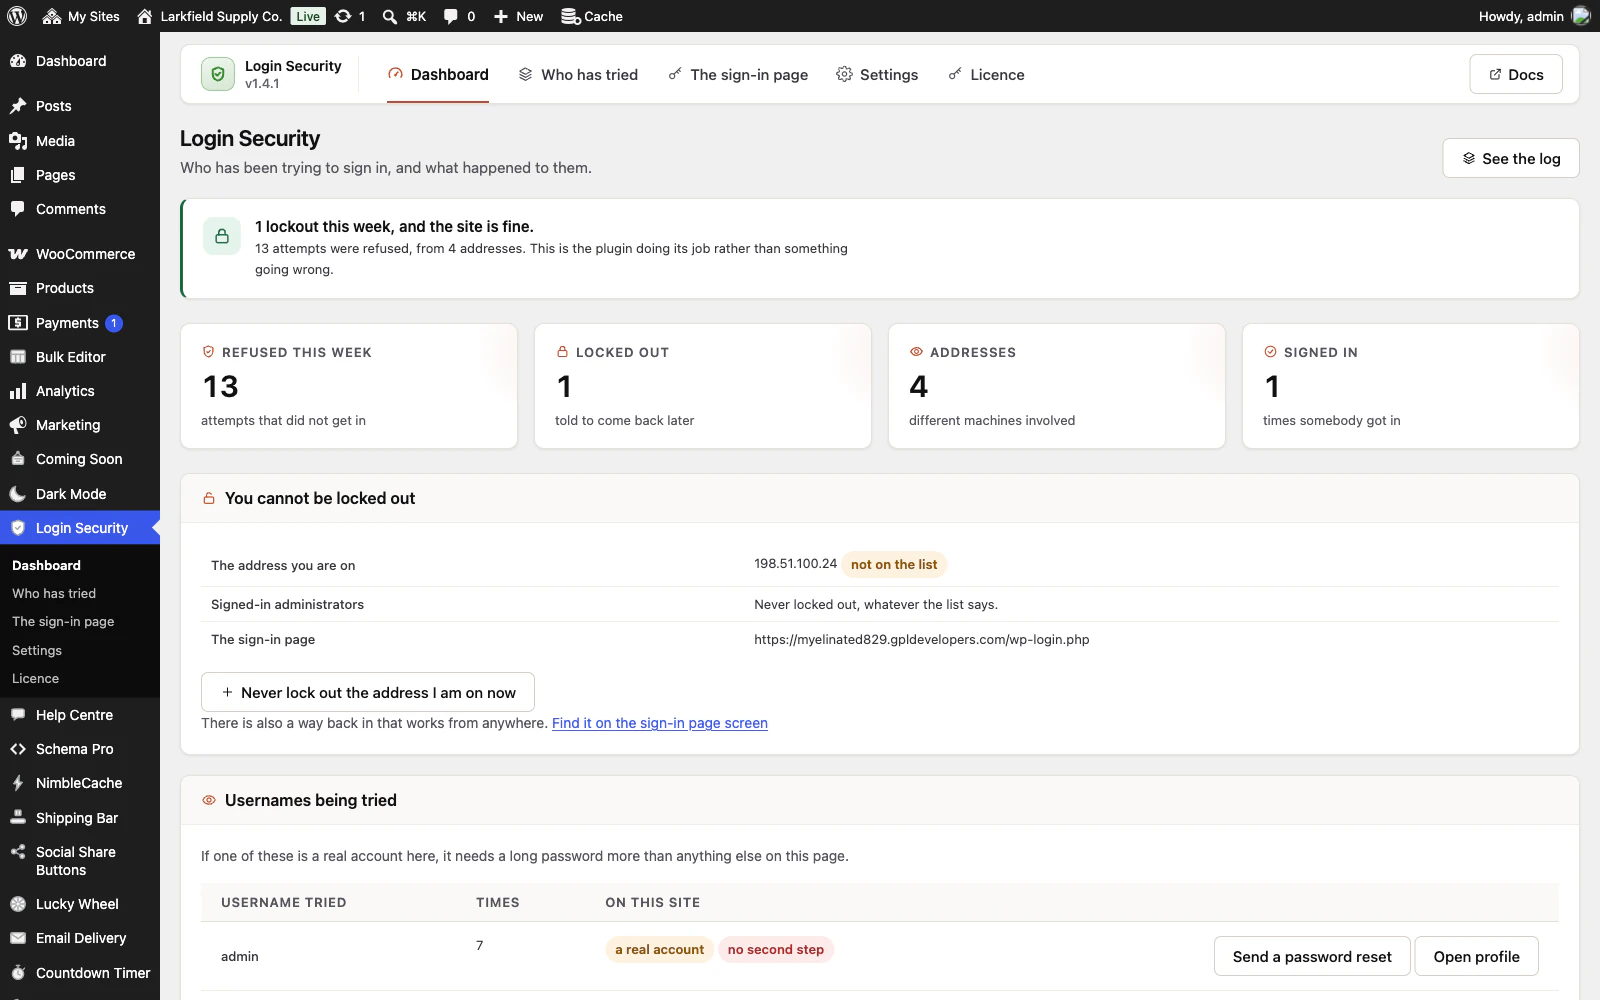
Almost certainly not. A lockout email means somebody tried passwords and was stopped, which is the plugin working rather than something going wrong. Any site that has been online for a few weeks gets this.
It is worth a look when the username being tried is a real account here, or when the same address is back day after day. The email names the address the attempt came from and says why the lockout happened. When one username was tried from many addresses, the reason names that username, so check whether it is an account on your site. An address coming back shows from one day's email to the next, and the Who has tried screen has the rest while Record every attempt is on.
Still stuck? Ask the developers who wrote it. We aim to reply within one business day.
 Login Security
Stop the machines guessing at your passwords, and see exactly who has been trying.
From $19 a year · every feature · 30-day refund