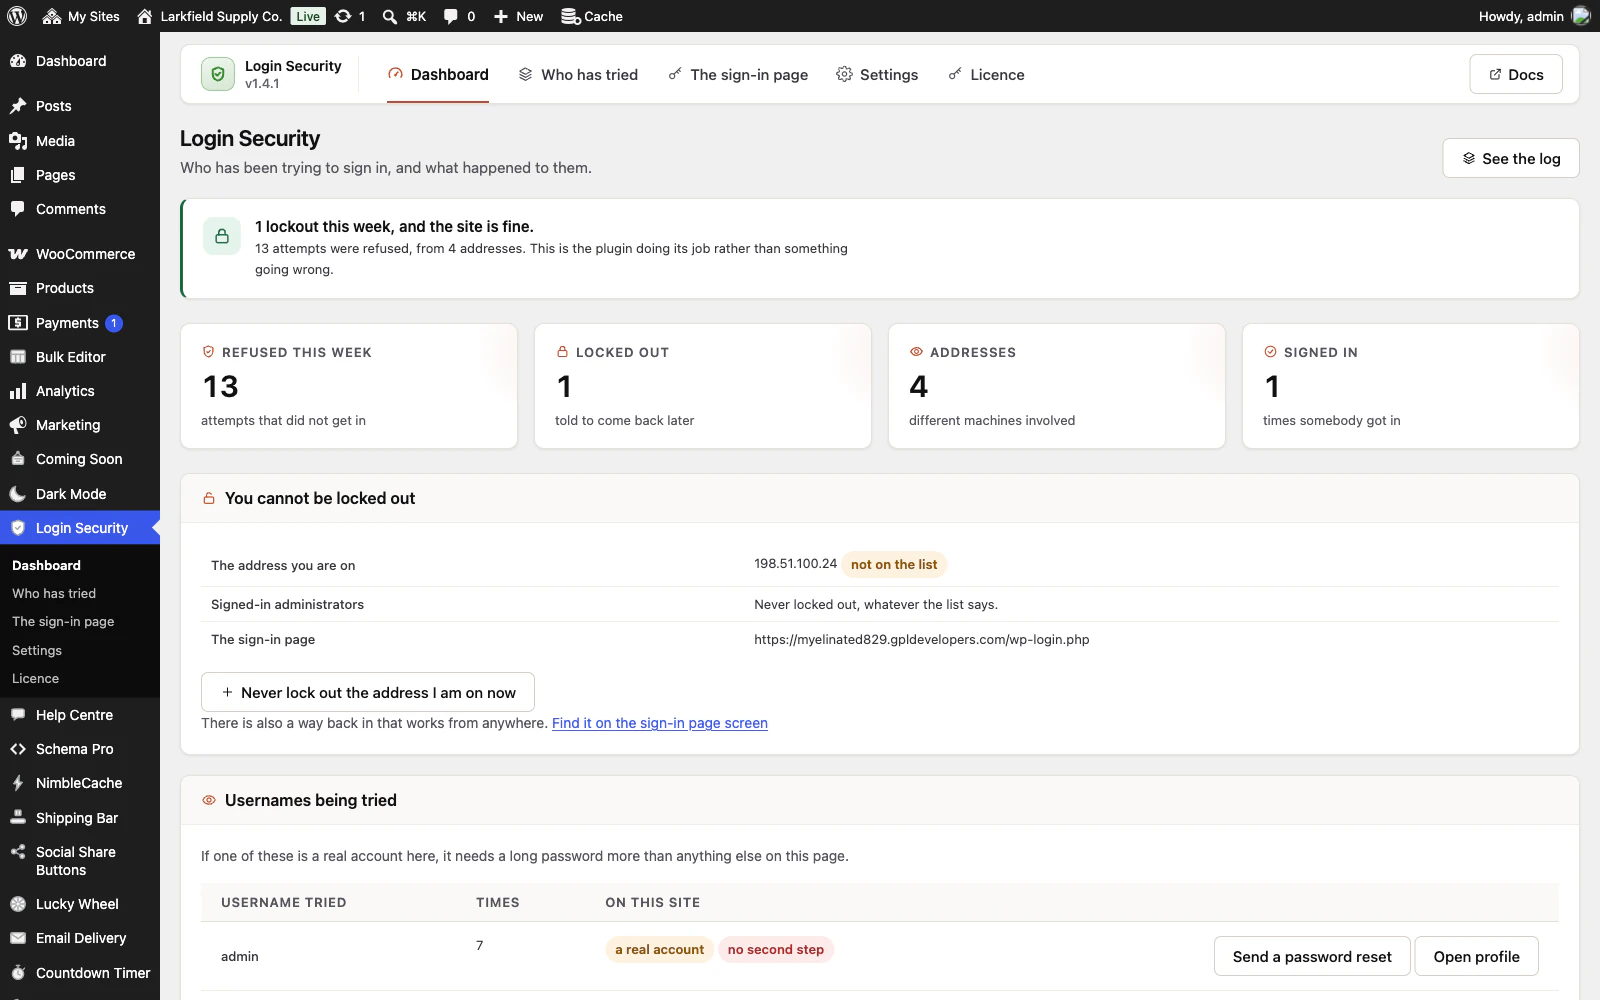
It stops guessing, which is the overwhelming majority of what arrives at a WordPress sign-in page. It does not stop somebody who already has your password — from a reused password, a phished one, or a leak somewhere else.
Nothing in this plugin is a substitute for long, unique passwords on the accounts that matter, and two-factor sign-in on top of them. What it does is handle the thousands of automated attempts that arrive anyway, and tell you when something unusual is happening.
Still stuck? Ask the developers who wrote it. We aim to reply within one business day.
 Login Security
Stop the machines guessing at your passwords, and see exactly who has been trying.
From $19 a year · every feature · 30-day refund