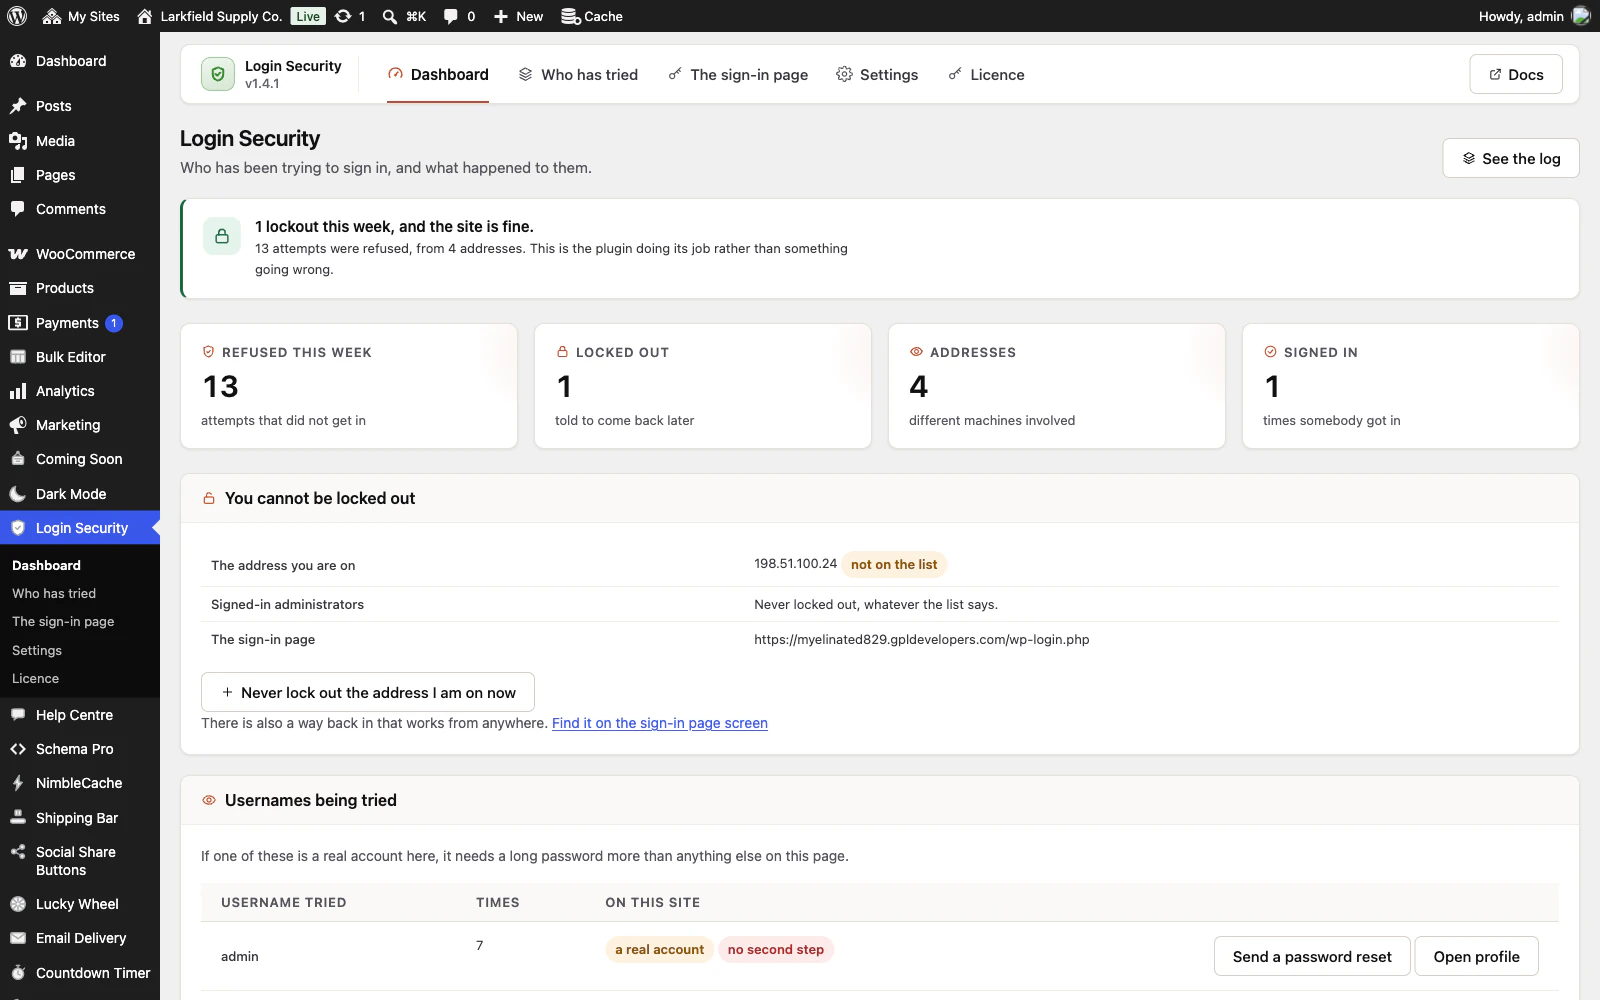
The opposite, on a site the machines have found. An attempt from a locked-out address is refused before WordPress looks up the user and long before it checks a password — a password hash is deliberately slow, and refusing early is the difference between five hundred slow operations a minute and five hundred database reads.
On the front of your site it does nothing at all: nothing loads for visitors, and no query runs on a page that is not a sign-in.
Still stuck? Ask the developers who wrote it. We aim to reply within one business day.
 Login Security
Stop the machines guessing at your passwords, and see exactly who has been trying.
From $19 a year · every feature · 30-day refund