All 31 Login Security answers

See every answer

Answer

Why not just use a CAPTCHA?

Updated Login Security 1.6.0Tested with WordPress 7.1

They are not exclusive, and a CAPTCHA solves a different problem. A CAPTCHA makes each attempt cost the attacker something; a lockout makes the attempts stop entirely after five. The one thing a CAPTCHA cannot do is tell you what has been happening, which is half of what this plugin is for.

This plugin does not include one, deliberately — every CAPTCHA worth having is somebody else's service, loaded on your sign-in page, watching your visitors.

Still stuck? Ask the developers who wrote it. We aim to reply within one business day.

Login Security

Stop the machines guessing at your passwords, and see exactly who has been trying.

From $19 a year · every feature · 30-day refund
Buy Login SecuritySee the plugin

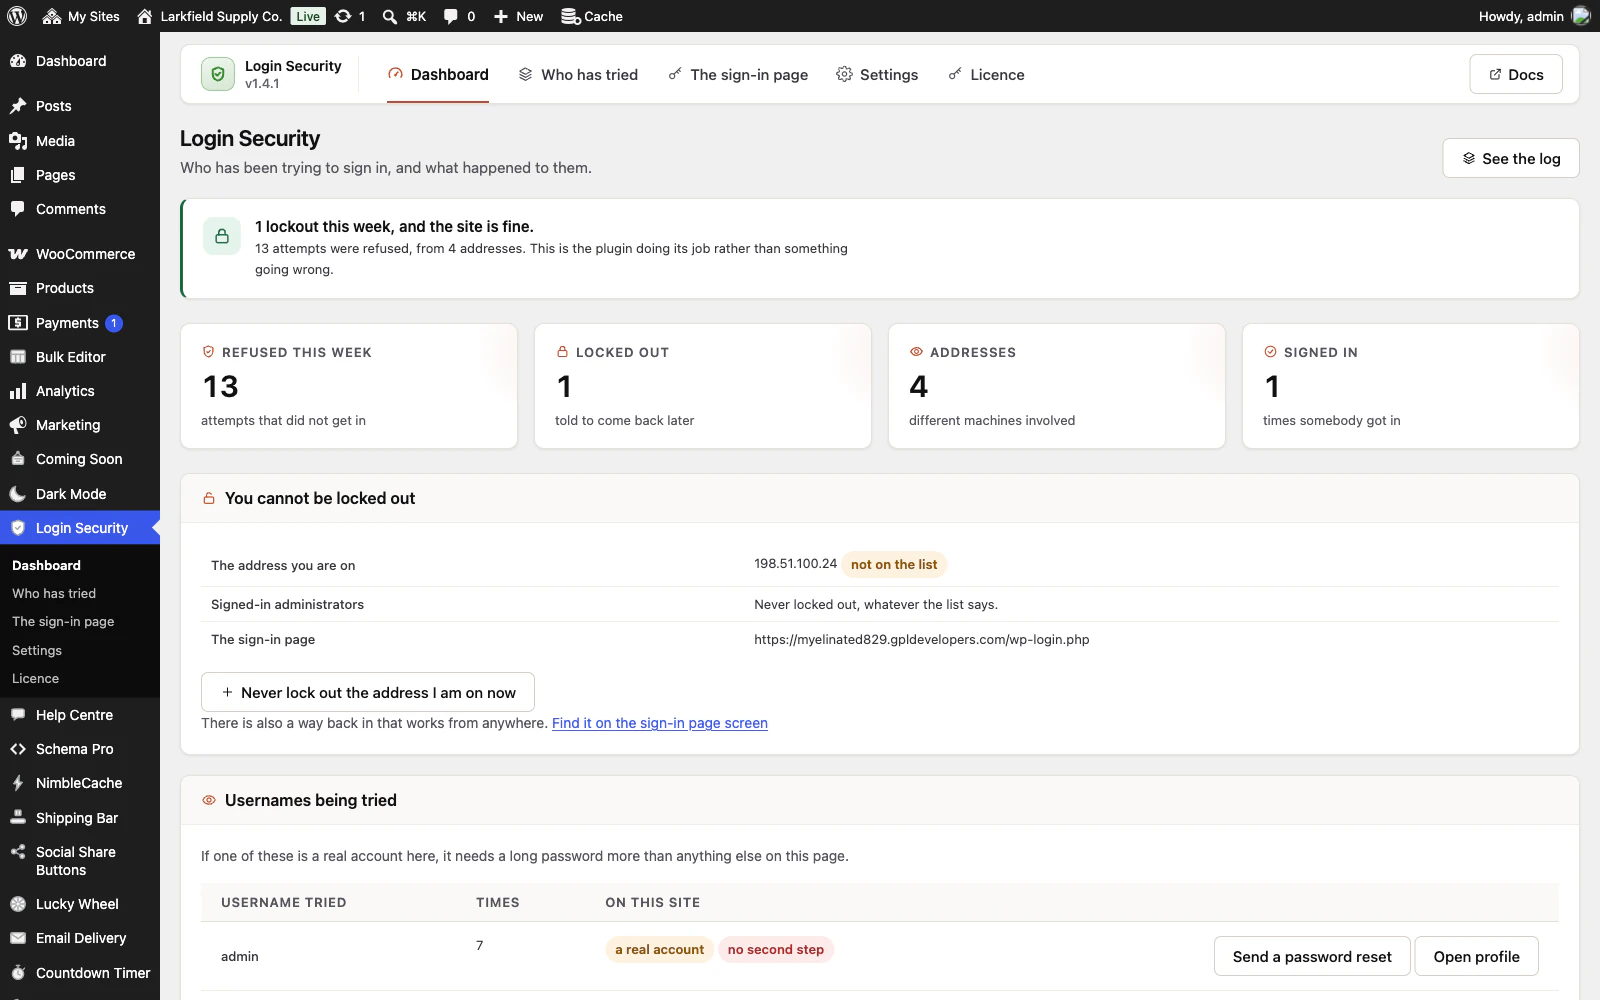
The Login Security dashboard in WordPress admin. A green notice reads 1 lockout this week, and the site is fine: 13 attempts were refused, from 4 addresses. Four cards show 13 refused this week, 1 locked out, 4 addresses and 1 signed in. A panel headed You cannot be locked out lists the address you are on, that signed-in administrators are never locked out, and the sign-in page, with a Never lock out the address I am on now button. Below it, Usernames being tried shows admin tried 7 times, marked a real account and no second step.