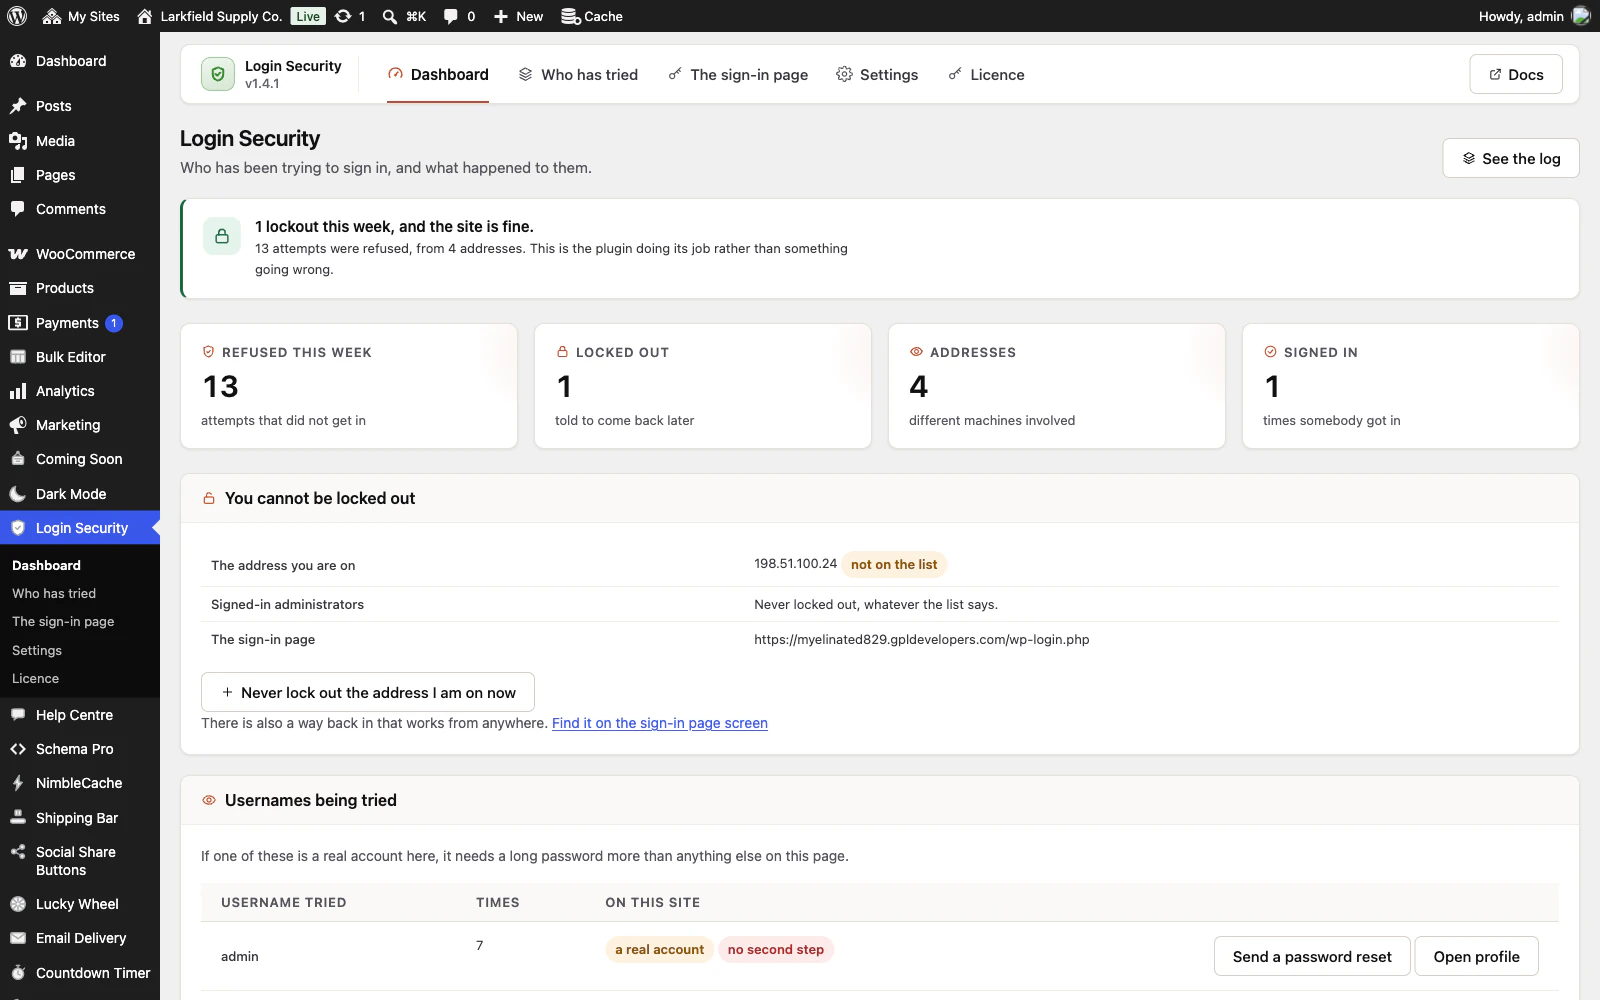
Login Security gives you four ways back in, and none of them needs the admin screens. In the order they are quickest:
- The recovery link. If you copied it somewhere when you set the plugin up, open it. It trusts whatever address you are on for an hour, then sign in with your password as normal.
- A different connection. The lockout is per address, so a phone off wi-fi is usually a different address entirely.
- WP-CLI, if your host gives you a terminal:
wp login-security unlocklifts every lockout on the site, including on hosts that keep them in an object cache such as Redis, and the count of failed attempts starts again. - Wait. The first lockout is twenty minutes by default, and the screen tells you how long is left.
If you have none of those, your host's support can run the WP-CLI line or deactivate the plugin from the file manager: renaming its folder in wp-content/plugins/ switches it off and loses nothing.
Related: Login Security docs: The way back in
Still stuck? Ask the developers who wrote it. We aim to reply within one business day.
 Login Security
Stop the machines guessing at your passwords, and see exactly who has been trying.
From $19 a year · every feature · 30-day refund